What does 2-of-3 multisig mean?
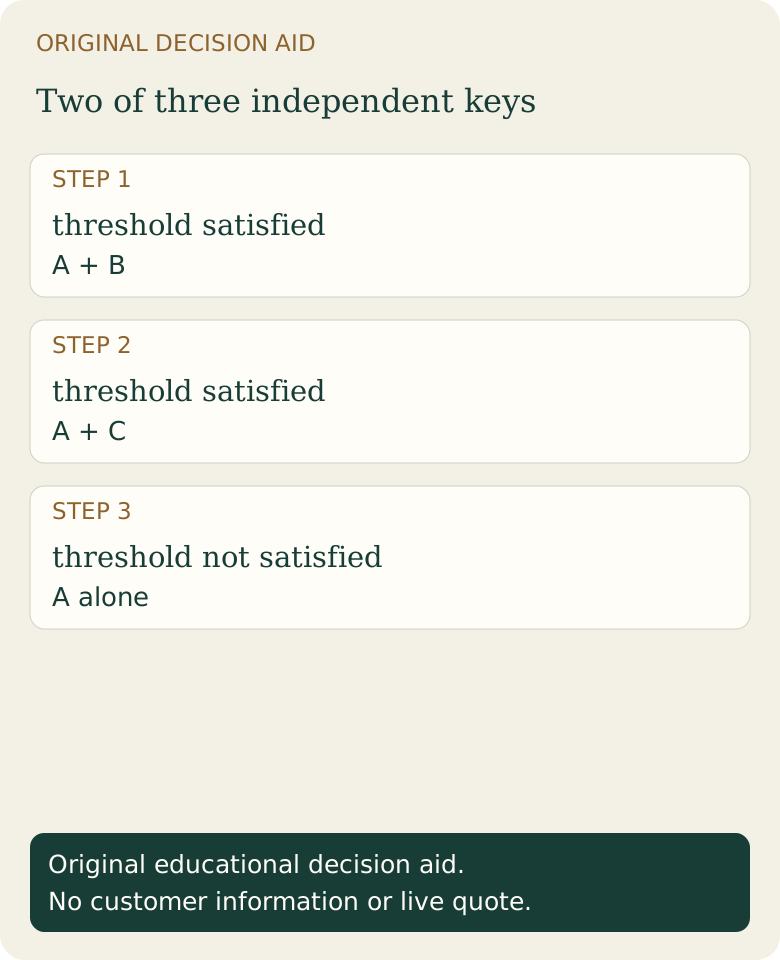
BIP 11 describes an m-of-n signature policy. In a simple 2-of-3 example, keys A, B and C participate in the policy and two are required to authorize a spend. Three copies of one seed are still copies of one key, not three independent cosigners.
The coordinator assembles wallet information and transactions; signing devices provide signatures under the policy. A watch-only coordinator may show history and prepare a transaction without holding enough secrets to spend. BIP 174 defines the partially signed transaction format used to exchange transaction and signing information.
Original matrix: which losses can a simple 2-of-3 plan tolerate?
This hypothetical matrix assumes independent uncompromised keys, a recoverable wallet configuration and no extra conditions. It is policy arithmetic, not a test of any product or a guarantee about theft, coercion or device failure.
Scroll across the table to see all columns.
| Available secrets | Threshold met? | Remaining problem |
|---|---|---|
| A + B + C | Yes | Protect all three; recovery still needs the policy. |
| A + B; C lost | Yes | Restore safely and consider a new policy after a permanent loss. |
| Only A; B and C lost | No | One signer cannot satisfy a two-signature threshold. |
| Two devices, same seed | Not necessarily | Two devices may represent only one distinct key. |
| Two secrets, no wallet configuration | Not established | Reconstruct the correct policy and addresses before spending. |
What should a recovery inventory contain?
Record the threshold, network, script type, each cosigner’s public wallet information, derivation details and key ordering as required by the chosen wallet. Preserve its supported configuration export or descriptor and instructions for finding the signing backups. Keep public configuration private too: it can expose addresses and history.
Keep secret backups and recovery instructions separated according to a deliberate threat model. Putting every seed and configuration in one unprotected cloud folder defeats much of the separation. Conversely, hiding components so thoroughly that your authorized recovery process cannot find them creates a loss risk. Do not place actual secrets in this page or an online worksheet.
How do you evaluate a multisig wallet without trusting a “best” list?
Use the current Ledger/Sparrow setup instructions as one documented configuration example, not our tested recommendation or a universal compatibility list. Check the exact firmware, coordinator version, address verification, supported policy export and replacement-device process.
Before funding, rehearse a recovery with disposable test material in the supported test environment. Ask whether a different coordinator can import the configuration, how each signer verifies the destination and change, and what happens when a vendor is unavailable. We have not performed a hardware comparison or reviewed specific products hands-on for this guide.
Is multisig the right first wallet?
A novice who cannot recover a single-key wallet may add more failure points by immediately adopting multisig. Compare hot and cold storage and custodial versus self-custody responsibilities first. More keys do not automatically mean a better recovery plan.
Fiat2Bitcoin does not hold a cosigning key, approve customer wallet transactions or provide a multisig recovery service. A purchase provider’s destination checks remain separate from your wallet’s signing policy.
Sources & further reading
These sources explain the payment systems and rules discussed in this guide. For your purchase, check the provider’s current offer and terms.
Published by Fiat2Bitcoin. Worked examples use fictional figures and records; they are not current prices or customer transactions. How we prepare our guides.